Communicating Cyber Risk to Business Leaders: 4 Proven Strategies That Bridge the Gap
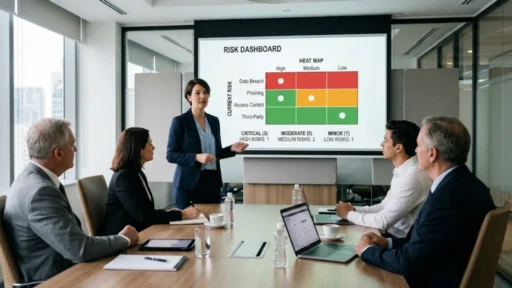
Communicating cyber risk in terms executives understand is one of the toughest challenges security and compliance teams face. In the realm of cyber risk, security and risk management leaders often struggle to connect the dots with business stakeholders, causing a significant disconnect. The key to bridging this gap lies in effective communication. Here are some strategies to consider for communicating cyber risk to business leaders:
Understand the Risk Appetite of the Audience
As stated in the Forbes article titled “Effectively Communicating Cyber Risk with Business Leaders”, “Risk appetite refers to the extent of risk an organization is prepared to tolerate in pursuit of its strategic goals. Recognizing that operating without any risk is unrealistic, organizations engage in a delicate balance between accepting certain risks and mitigating others whenever possible.” Before presenting to business stakeholders, security and risk teams must understand their organization’s risk appetite to effectively communicate updates and offer actionable recommendations. Communicating cyber risk without that context often produces recommendations that strike leadership as either alarmist or too casual.
Become an Effective Storyteller to Make Cyber Risk Relevant
The same Forbes article also mentions, “Effective storytelling aims to achieve three primary objectives: informing and educating, influencing decisions and altering behaviors.” Although technical jargon might not capture a business audience’s interest right away, linking these topics to how they impact the bottom line or customers can make business leaders more receptive. When communicating cyber risk, a short, concrete example of how an incident could disrupt operations or customers will usually land better than a list of technical vulnerabilities.
Include Qualitative Elements
According to the Harvard Business Review article titled “The Art of Communicating Risk”, “firms facing the question of whether and how to communicate risk often err too far in either direction. When organizations alert their customers to every potential risk, they create notification fatigue… When firms do the opposite… Customers interpret time lags as incompetence, or worse, as obfuscation and protection of corporate reputations at the expense of protecting customers.”
Master Speaking on a Business Level When Communicating Cyber Risk
The Forbes article suggests, “Cyber and risk leaders must craft their communication to resonate with a business audience.” Using techniques from behavioral science, leaders can communicate uncertain risks in a way that will protect customers and foster trust. This could involve strategies such as framing the information in a way that is relevant to the audience, using clear and simple language, and providing actionable steps that the audience can take to manage the risk.
In conclusion, effectively communicating cyber risk with business leaders is a delicate balance of understanding the audience’s risk appetite, storytelling, including qualitative elements, and speaking on a business level. By mastering these strategies, cyber and risk leaders can ensure their messages are not only heard but also understood and acted upon.
Give Employees a Safe Way to Raise Cyber Risk Concerns
Communicating cyber risk isn’t only a top-down exercise. Employees are often the first to notice phishing attempts, mishandled data, or policy shortcuts that create exposure, and they need a confidential way to speak up. Red Flag Reporting’s hotline and case management tools give your people a secure channel to raise concerns and give your leadership a clear record of what has been reported, helping you protect your reputation and respond with confidence. Contact us today to learn how Red Flag Reporting can support your organization.
Frequently Asked Questions About Communicating Cyber Risk
What does communicating cyber risk to business leaders involve?
It means translating technical findings, such as vulnerabilities, threats, and incidents, into business terms like revenue, operations, customers, and reputation. Effective cyber risk communication also ties each issue to the organization’s risk appetite and ends with clear, actionable recommendations.
Why do security teams struggle to communicate cyber risk to executives?
Security professionals tend to speak in technical language and focus on threats, while executives focus on business outcomes and trade-offs. Without a shared vocabulary, important warnings can be misunderstood, underestimated, or tuned out entirely.
What is risk appetite, and why does it matter when communicating cyber risk?
Risk appetite is the amount of risk an organization is willing to accept in pursuit of its strategic goals. Knowing it allows security teams to frame recommendations in a way leadership can act on, rather than presenting every risk as equally urgent.
How can storytelling improve cyber risk communication?
Stories, analogies, and realistic scenarios help non-technical audiences understand how a cyber incident could actually affect the business. A concise narrative is easier to remember and more likely to influence decisions than a technical report.
How can employees help an organization manage cyber risk?
Employees often spot warning signs first, such as suspicious emails, careless data handling, or workarounds to security policies. Giving them a confidential reporting channel, such as an ethics and compliance hotline, encourages them to raise concerns early so leadership has a more complete picture of the organization’s risk.
Reach Us
Red Flag Reporting
P.O. Box 4230, Akron, Ohio 44321
Tel: 877-676-6551
Fax: 330-572-8146